Information SecurityUnit 28 min read
Security Threats & Attacks: Types, Methods & Real-World Impacts
Unit 2 of Information Security explores the classification of security threats (passive/active, internal/external), common attack methods (phishing, DoS, MITM, malware), their mechanisms and impacts, and real-world case studies from Nepalese and global systems. Learn how attackers exploit vulnerabilities in networks, a
1. Classification of Security Threats
Security threats are categorized based on nature, origin, and intent. Understanding these helps in designing targeted defenses.
1.1 By Nature of Attack
Threats can be passive or active:
Passive Attacks: Eavesdropping, traffic analysis, monitoring (no modification of data).
- Example: An attacker uses a packet sniffer (like Wireshark) to capture unencrypted emails on a public Wi-Fi.
- Impact: Data leakage (e.g., login credentials, financial details).
flowchart TD
  A["Passive Attack"] --> B["Eavesdropping"]
  A --> C["Traffic Analysis"]
  B --> D["Sniffing Tools: Wireshark, tcpdump"]
  C --> E["Inferring Patterns: Timing, Frequency"]
Active Attacks: Modification, deletion, or fabrication of data (e.g., man-in-the-middle (MITM), denial-of-service (DoS)).
- Example: A hacker alters a Khalti payment transaction to redirect funds to their account.
- Impact: Financial loss, data corruption, system crashes.
1.2 By Origin of Threat
Threats originate from internal or external sources:
| Type | Description | Example | Risk Level |
|---|---|---|---|
| Internal | Insiders (employees, contractors) with authorized access. | A bank employee leaking customer data. | High (70% of breaches) |
| External | Hackers, competitors, or cybercriminals. | A DDoS attack on NTC’s website. | Medium-High |
1.3 By Intent
- Accidental: Human error (e.g., misconfigured firewall).
- Deliberate: Malicious intent (e.g., ransomware, phishing).
2. Common Security Attacks
2.1 Social Engineering Attacks
Exploits human psychology rather than technical vulnerabilities.
- Phishing: Fake emails/websites to steal credentials.
- Example: A WhatsApp message claiming "Your eSewa account is locked—click here to verify."
- Defense: Multi-Factor Authentication (MFA), user training.
- Spear Phishing: Targeted at specific individuals (e.g., CEO fraud in banks).
- Baiting: Offering something enticing (e.g., free software with malware).
- Example: A USB drive labeled "Salary Slip 2024" left in an office.
2.2 Network-Based Attacks
A. Denial-of-Service (DoS) and Distributed DoS (DDoS)
- Mechanism: Floods a system with traffic to crash it.
- Example: A DDoS attack on Nepal Stock Exchange (NEPSE) during trading hours.
- Types:
- SYN Flood: Exploits TCP handshake.
- Ping of Death: Oversized ICMP packets.
- UDP Flood: Sends fake UDP packets.
sequenceDiagram
  participant Attacker as Attacker (Botnet)
  participant Victim as Target Server (e.g., NEPSE)
  loop DDoS Attack
    Attacker->>Victim: SYN Request (Fake IP)
    Victim->>Attacker: SYN-ACK (Unresponsive)
    Attacker->>Victim: Never sends ACK
  end
  Note right of Victim: Server resources exhausted → Crash
B. Man-in-the-Middle (MITM) Attacks
- Mechanism: Intercepts communication between two parties.
- Example: A hacker on a public Wi-Fi in Thamel intercepts Khalti transactions.
- Tools: ARP spoofing, SSL stripping.
- Defense: HTTPS (TLS/SSL), VPNs.
C. Session Hijacking
- Mechanism: Steals a valid session ID to impersonate a user.
- Example: An attacker hijacks a logged-in Pathao driver’s session to access passenger data.
- Prevention: Short session timeouts, secure cookies.
2.3 Malware Attacks
Malicious software designed to damage, disrupt, or gain unauthorized access.
| Type | Description | Example | Impact |
|---|---|---|---|
| Virus | Attaches to clean files. | ILOVEYOU virus (2000) spread via email. | Data corruption, system crash. |
| Worm | Self-replicating, spreads without user action. | Morris Worm (1988) exploited Unix vulnerability. | Network congestion, downtime. |
| Trojan Horse | Disguised as legitimate software. | Fake "Daraz Discount Tool" with keylogger. | Remote access, data theft. |
| Ransomware | Encrypts data, demands payment. | WannaCry (2017) hit hospitals globally. | Data loss, financial extortion. |
| Spyware | Monitors user activity. | Keyloggers in "free" PC cleaning tools. | Credential theft, privacy loss. |
3. Real-World Applications & Case Studies
3.1 eSewa & Khalti: Phishing & MITM Risks
- Scenario: A user logs into eSewa via a fake website (phishing) or an MITM attack on a café’s Wi-Fi.
- Attack Flow:
- User enters credentials on a fake eSewa login page.
- Attacker captures credentials and logs into the real account.
- Transfers money to their Khalti wallet.
- Prevention:
- Always use official apps (not browser-based logins on public Wi-Fi).
- Enable OTP + Biometric authentication.
3.2 NTC & Ncell: DDoS Attacks on Critical Infrastructure
- Scenario: During the 2021 COVID-19 lockdown, NTC’s website was targeted with a DDoS attack, causing service disruptions.
- Why It Matters:
- Botnets (zombie PCs) were used to flood NTC’s servers.
- Impact: Delayed internet access for millions.
- Defense Strategies:
- Cloud-based DDoS protection (e.g., Akamai).
- Rate limiting on login attempts.
3.3 Daraz & Pathao: Session Hijacking in E-Commerce
- Scenario: A hacker steals a Daraz session cookie while a user is browsing.
- How It Works:
- User logs into Daraz on a shared PC (e.g., cyber café).
- Attacker uses XSS (Cross-Site Scripting) to steal the session cookie.
- Hijacks the session to place orders or change delivery addresses.
- Solution:
- HTTP-only cookies (inaccessible to JavaScript).
- Short-lived session tokens.
4. Defense Mechanisms Against Attacks
| Attack Type | Prevention Technique | Example Implementation |
|---|---|---|
| Phishing | User training, email filters. | eSewa’s SMS alerts for login attempts. |
| DDoS | Firewalls, rate limiting, CDNs. | NTC uses Cloudflare for DDoS protection. |
| MITM | VPNs, HTTPS, certificate pinning. | Khalti enforces HTTPS for all transactions. |
| Malware | Antivirus, sandboxing, updates. | Windows Defender + regular OS patches. |
| Session Hijacking | Secure cookies, short sessions. | Pathao uses JWT with expiry times. |
5. Worked Example: Analyzing a Phishing Email
Scenario: You receive an email from "Nepal Rastra Bank" with the subject: "Your Account Has Been Suspended – Click Here to Verify."
Step-by-Step Analysis
- Check Sender Address:
- Legitimate:
noreply@nrb.org.np - Phishing:
nrb_support123@gmail.com→ Red Flag.
- Legitimate:
- URL Inspection:
- Hover over the link:
http://fake-nrb-verification.com→ Not HTTPS, suspicious domain.
- Hover over the link:
- Content Clues:
- Urgent language ("immediate action required").
- Generic greeting ("Dear Customer" instead of your name).
- Action:
- Do not click. Report to IT/security team.
- Verify via official NRB website or hotline.
6. Exam Tip: How This Unit is Tested
- Definitions & Classifications:
- Expect short-answer questions on:
- Difference between passive vs. active attacks.
- Types of malware (virus, worm, Trojan).
- Expect short-answer questions on:
- Scenario-Based Questions:
- Case study: "A Daraz user reports unauthorized orders. Explain possible attacks and defenses."
- Solution: Describe session hijacking and secure cookies.
- Diagrams & Flowcharts:
- Draw a sequence diagram for:
- MITM attack (e.g., on Khalti).
- DDoS attack (botnet → victim).
- Draw a sequence diagram for:
- Real-World Applications:
- Relate attacks to Nepali systems (e.g., NEPSE hack, eSewa phishing).
- Example question: "How would you secure a bank’s online transaction system from MITM attacks?" Answer: Use TLS 1.3, HSTS, and hardware security modules (HSMs).
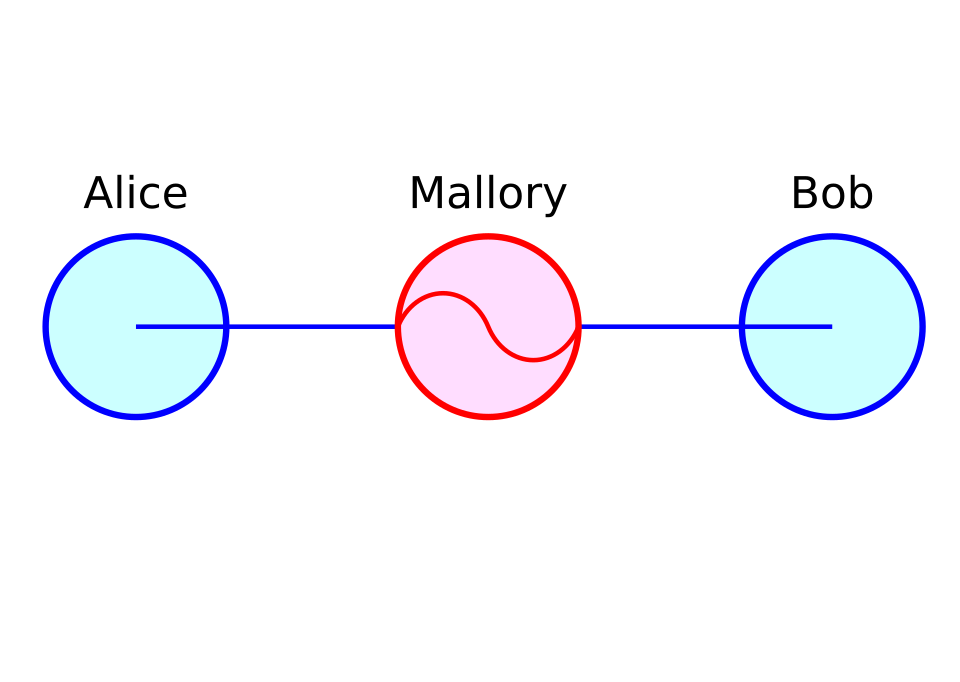 A labeled MITM attack flow showing attacker intercepting communication between a user and a bank. (Image: Miraceti, CC BY-SA 3.0, via Wikimedia Commons)
Based on the TU BITM syllabus for Information Security (IT244), unit 2.
Discussion
Loading…